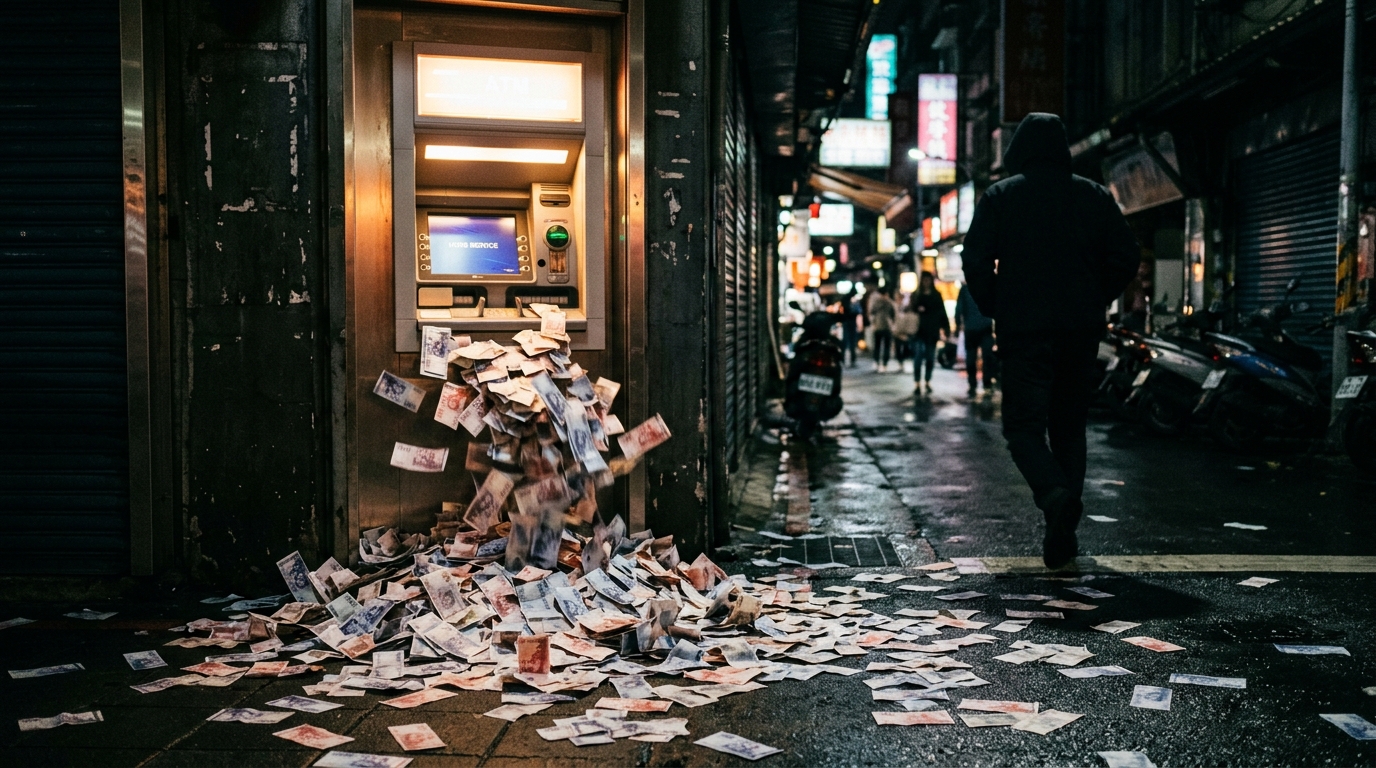
On one side, hackers capable of crossing an entire continent in a few clicks, infiltrating the very digital core of an Asian bank from a London-based server. On the other, a handful of Taiwanese police armed with nothing more than CCTV footage, solving the case in a mere week where months of fruitless investigation might have been expected. This is the paradox at the heart of this bank cybercrime heist, which has gone down in the annals: the more technologically sophisticated the crime, the more trivial the human flaw that betrays it appears. In July 2016, this contrast took a spectacular form in Taiwan, where 41 ATMs were spitting out bundles of cash without any bank card ever being inserted. An attack of surgical precision, orchestrated from the other side of the world, but ultimately stopped by the most banal tool imaginable: the surveillance camera.
- In July 2016, 41 ATMs of First Commercial Bank were hacked via the Ripper malware, introduced through the London branch’s call-record server, enabling cash withdrawals initiated by a mobile phone without a bank card.
- The alert did not come from banking systems but from witnesses spotting suspicious individuals; the investigation, based on 1500 hours of surveillance footage and 30,000 phone records, was resolved in just seven days.
- The attack, linked to the international Cobalt network that targeted more than a hundred financial institutions worldwide, led to the recovery of NT$77.48 million of the NT$83.27 million stolen.
- The night the ATMs started spewing money on their own
- Ripper, the malware that spoke directly to the machines
- Video surveillance, the blind spot neglected by cybercriminals
- What this Taiwanese heist changed in global banking security
The night the ATMs started spewing money on their own
Between July 9 and 11, 2016, something abnormal occurred in several branches of the First Commercial Bank, one of Taiwan’s largest banks. In a single night, 41 ATMs across 22 branches began dispensing cash continuously, with no standard transaction appearing in the registers. No card inserted, no PIN entered: the machines obeyed an invisible order, coming from nowhere and everywhere at once. The surreal night’s total stood at NT$83.27 million, the equivalent of several millions of euros stolen in just a few hours.
On site, individuals from Eastern Europe methodically retrieved the bills, stuffing them into bags before vanishing into the Taiwanese night. What would later be revealed is that these men were only the visible face of a much larger network: in total, 22 suspects from nine different countries, mainly Latvia, Estonia, Romania, and Russia, would be identified by investigators. Nineteen of them would flee the country soon after the heist, while three would stay on site to attempt to discreetly exfiltrate the cash, hidden in hotel rooms.
Ripper, the malware that spoke directly to the machines
To understand how such a robbery could be carried out without physical intrusion or bank cards, one must trace the thread back to London. It was via the British branch of the First Commercial Bank that the attackers found their entry point. Their initial target wasn’t the ATMs themselves but a far more discreet link: the call-recording server of the London branch. Once this server had been compromised, it served as a relay, a digital springboard, to bounce into the system that manages the software updates of the ATMs distributed thousands of kilometers away in Taiwan.
The malware deployed in this operation would become notoriously famous a few weeks later: Ripper. Identified by the cybersecurity company FireEye after similar attacks observed in Thailand, this program targeted ATMs manufactured by the German company Wincor Nixdorf. Its peculiarity lay in its ability to completely bypass the traditional banking transaction circuit: rather than requiring a card, it allowed withdrawals directly via mobile devices, turning every infected ATM into a mere cash dispenser obeying a remote command. The mules then only had to stand before the machine and enter a specific code to trigger the cash ejection, leaving no trace of traditional banking activity.
Video surveillance, the blind spot neglected by cybercriminals
Here lies the paradox that makes this case so fascinating: criminals capable of bypassing the security protections of an international bank apparently did not foresee a brutally human detail. It was not the fraud-detection algorithms nor the automated alerts of the banking system that raised the alarm, but ordinary citizens, intrigued by the suspicious behavior of unfamiliar individuals loitering near ATMs at night with bags in hand. It is these spontaneous testimonies that triggered the initial alert to the police.
From that signal, the investigation accelerated with remarkable speed. Taiwanese police reviewed more than 1500 hours of surveillance footage, cross-referenced more than 30,000 phone records, and leveraged trace evidence left by the suspects in the hotels where they sought refuge. Traffic cameras and those placed near bank branches allowed reconstituting, minute by minute, the movements of the three individuals who remained on the island. The result: the case was solved in seven days, a record time considering the technical complexity of the initial hack. Even better, a civilian eventually found a bag containing part of the loot, enabling authorities to recover around NT$77.48 million of the NT$83.27 million stolen, nearly the entire sum.
What this Taiwanese heist changed in global banking security
This heist was in fact only the tip of a much larger iceberg. Investigations by the cybersecurity firm Group-IB linked the attack to an international criminal syndicate nicknamed Cobalt, suspected of targeting more than a hundred financial institutions worldwide. Two years after the events, the brain behind this network, a Ukrainian national, was finally arrested in Spain. European authorities cited a global damage figure exceeding one billion euros, a number that underscores the true scale of this organization, of which the Taiwanese caper was only one episode among many.
The case left a lasting mark on the banking sector, driving many institutions to rethink the security of their software-update servers, often regarded as secondary links and thus less protected than the transaction systems themselves. It also recalled a simple but essential lesson: no matter how sophisticated a cyberattack, someone is still exposed physically at some moment—whether in front of an ATM or in a hotel corridor. The three accomplices who stayed in Taiwan were eventually sentenced to prison on the island, while the rest of the network continued to operate elsewhere for several more years.
This heist remains in memory as a vivid illustration of how porous the boundary between the digital and the physical world can be, even for the most seasoned cybercriminals. Today, as techniques for bank hacking continue to evolve, this Taiwanese case continues to serve as a benchmark in cybersecurity training, a reminder that the best digital protections can never replace the vigilance of a passing bystander. One question still lingers: how many other networks like Cobalt are still operating today, hidden from view, awaiting their own misstep?